ISO Standards for Manufacturing: Complete Compliance Guide for 2026 [ISO 9001, 13485 & More]
ISO 9001:2026, ISO 13485, and ISO 8000 explained for manufacturers, plus how PIM keeps product data audit-ready and traceable across channels.
Table of Contents
Key Terms to Know
ISO 9001 and ISO 13485 set the rules for how manufacturers prove quality. Most teams focus on the factory floor. The weak spot is usually somewhere else, and that is the product data that describes what the factory makes.
If you make, distribute, or sell physical products, you will run into ISO standards sooner or later. More than 1 million ISO 9001 certificates are in force around the world, and many buyers treat certification as a basic requirement before they will sign a supplier.
What most compliance guides leave out is that these standards also expect your product information to be controlled, accurate, and traceable. That gets hard fast with thousands of SKUs. A SKU (stock keeping unit) is the code that identifies each product variant, and the data for each one has to reach distributors, digital showrooms, and e-commerce channels.
The bar went up in 2026. The FDA Quality Management System Regulation (QMSR) took effect on February 2, 2026. ISO 14001:2026 was published on April 15, 2026. Then ISO launched ISO 9001:2026 on September 16, 2026. Each one asks for more documented, traceable evidence, and much of that evidence is product data.
Quick Read: ISO Compliance in Manufacturing
ISO compliance means running your business to meet international standards published by the International Organization for Standardization (ISO), and being able to prove it with controlled records. The standards cover quality, safety, environmental performance, and traceability. For most manufacturers, the core standard is ISO 9001 for quality management. Medical device makers add ISO 13485. ISO writes the standards but does not certify anyone itself. An independent, accredited certification body does the audit and issues the certificate.
The Standards Manufacturers Use
ISO is an independent, non-governmental organization. It has published more than 26,500 International Standards and related documents, covering almost every industry. When a company earns ISO certification, it shows that a product, service, system, or process meets an agreed international benchmark. That shared benchmark makes it easier for companies in different countries to trust each other and trade.
For manufacturers, the standards set out documented ways to handle quality, safety, environmental impact, and data integrity. A certificate tells customers, distributors, and regulators that someone has checked those processes.
Demand is growing. Fact.MR estimates the global ISO certification market at $16.14 billion in 2024. It projects $66.25 billion by 2034, a compound annual growth rate (CAGR) of 15.2%. Many large multinational buyers expect suppliers to hold at least one ISO certificate, and certification is often required to bid on government contracts. For a manufacturer chasing international work, certification removes a common hurdle in supplier qualification.
The 2024 ISO Survey counted 1,474,118 valid ISO 9001 certificates, 676,232 for ISO 14001, 542,527 for ISO 45001, and 31,215 for ISO 13485. One caution: from 2024 onward, the survey uses data from IAF CertSearch, a global database of accredited certificates, so comparing these numbers with older editions can be misleading.
Here are the standards that come up most often in manufacturing:
| Standard | What It Covers | Who Usually Needs It |
|---|---|---|
| ISO 9001:2026 (replaces ISO 9001:2015 after a three-year transition) | Quality management systems | All manufacturers |
| ISO 13485:2016 | Quality management for medical devices | Medical device manufacturers |
| ISO 14001:2026 (replaces ISO 14001:2015 after a three-year transition) | Environmental management systems | Operations with sustainability goals or customer requirements |
| ISO 45001:2018 (revision underway) | Occupational health and safety | Any facility with physical risk |
| ISO 50001:2018 | Energy management | Energy-intensive plants |
| ISO 22000:2018 | Food safety management | Food production and packaging |
| ISO/IEC 27001:2022 | Information security | Connected and smart factories handling proprietary data |
| ISO 8000 | Master data and data quality | Manufacturers with complex product data |
ISO 9001 as the Quality Baseline
ISO 9001 is the most widely certified ISO standard in the private sector. Any company of any size can use it. It sets the requirements for a quality management system (QMS). A QMS is the set of documented processes a company uses to meet customer and regulatory requirements and to keep improving.
The standard rests on a few ideas:
- Focus on the customer, and keep improving.
- Think about risk, using the Plan-Do-Check-Act cycle to refine processes over time.
- Document processes and monitor how they perform.
- Make decisions based on evidence, not opinion.
- Make management accountable for quality and for the resources it needs.
Leadership support matters more than any single clause. Without it, nobody funds training, and a quality culture never takes hold.
The requirement that catches many manufacturers off guard is controlled documentation. ISO 9001 does not stop at process manuals. It also covers product specifications, calibration records, training logs, and supplier data. With hundreds or thousands of SKUs, that becomes a product data problem very quickly.
Most companies start with a gap analysis, a review of what their current processes are missing compared with the standard. It gives them a clear plan before they spend money. From there, consistent processes reduce variation, cut waste, and lower costs. Certification also builds credibility with new customers, especially when it is backed by strong product information management practices. In short, ISO 9001 is increasingly the price of entry to global markets, and because it is built around customer focus, it supports customer satisfaction and long-term trust.
The 2026 Edition
ISO published the sixth edition, ISO 9001:2026, on September 16, 2026. It updates the 2015 version rather than replacing it. It also uses ISO’s latest Harmonized Structure, a shared layout for management system standards, so it fits more easily alongside ISO 14001 and ISO 45001.
DNV’s summary of the revision highlights these changes:
- Top management must now promote quality culture and ethical behavior (Clause 5.1.1), and employees must be aware of both (Clause 7.3).
- Clause 6.1 now has subclauses, so risks and opportunities are handled separately.
- Requirements for planning and controlling changes to the QMS (Clause 6.3) are stronger.
- The 2024 climate change amendment to Clauses 4.1 and 4.2 is now part of the main text.
- Certified companies have three years to move over. ISO 9001:2015 certificates stop being valid after September 30, 2029.
For product teams, the stronger change management rules matter most. A new spec, a label edit, or a renewed certificate is a change to the evidence your QMS depends on. Auditors will look more closely at how those changes were planned, approved, and recorded.
Medical Devices Follow Stricter Rules
ISO 13485:2016 is the quality standard built for medical device makers. It asks for tighter document control, better traceability, and risk management focused on patient safety. Compared with ISO 9001, four differences stand out.
More documentation. ISO 13485 requires a medical device file for each device type or family, detailed purchasing records, and formal procedures for customer feedback.
A direct link to U.S. law. The FDA’s Quality Management System Regulation became effective on February 2, 2026. It replaced the older Quality System Regulation in 21 CFR Part 820 and incorporates ISO 13485:2016 by reference. In other words, the standard’s requirements now carry legal weight for devices sold in the United States. The FDA has also said it will not require ISO 13485 certificates, and having one does not exempt a manufacturer from FDA inspection.
The route into Canada and the EU. Health Canada made the Medical Device Single Audit Program (MDSAP) the only way to show compliance with its quality system rules. Since January 1, 2019, it has accepted only MDSAP certificates. MDSAP audits are built on ISO 13485 plus Canadian requirements. In the EU, EN ISO 13485 is a harmonised standard, a European standard officially recognized under EU law. Using harmonised standards is voluntary, but doing so gives a presumption of conformity with the Medical Device Regulation requirements they cover.
Risk management everywhere. ISO 13485 builds risk management into the whole product life cycle. The FDA points out that by bringing in ISO 13485:2016, the QMSR now specifically requires risk management.
The 2016 edition remains current, and certification body TÜV NORD reports that ISO 13485:2016 has been reconfirmed with no revision planned, remaining unchanged until April 2030. That gives device makers a stable target while they adjust to the QMSR.
Beyond Quality: Environment, Safety, Data, and Materials
Quality is only one part of the picture. Depending on what you make and where you sell, several other standards may apply.
ISO 14001 (environmental management). Part of the ISO 14000 family, ISO 14001 helps manufacturers reduce their environmental impact, manage waste, and meet environmental regulations. It is the second most certified ISO management system standard after ISO 9001, with 676,232 certificates in the 2024 ISO Survey. The new ISO 14001:2026 was published on April 15, 2026, with a three-year transition. It makes climate change a required element. It also adds biodiversity, resource availability, and pollution to the environmental aspects companies must consider, and asks for more control over upstream and downstream supply chains. In practice, environmental claims on products now need the same controlled evidence as quality claims.
ISO 45001 (occupational health and safety). This standard gives companies a framework to spot hazards, assess risks, and put controls in place so people are safer at work. A well-run system is designed to reduce accidents, which also means fewer disruptions and lower liability. The 2018 edition is now under revision, with a new edition expected in 2027.
ISO 50001 (energy management). Rising energy costs and sustainability targets make this one more relevant every year. It works alongside ISO 14001 to cut waste and improve energy efficiency.
ISO 22000 (food safety). It covers food safety across the supply chain. For food production and packaging, falling short can lead to costly recalls.
ISO/IEC 27001 (information security). As factories connect more machines and systems, production data and intellectual property become easier targets. ISO/IEC 27001 sets out how to protect them, including proprietary data that often sits in a Product Information Management (PIM) and DAM platform.
EN 10204 and ISO 10474 (material certification). People sometimes call this “ISO 10204,” but no such ISO standard exists. The correct reference is EN 10204, the European standard for the inspection documents that come with metallic products. Its international counterpart for steel products is ISO 10474. Both define the certificates and test reports that confirm what a material is made of. They matter most when material traceability is part of a contract or a regulation.
ISO 8000 (master data quality). This is the standard closest to product data. The ISO 8000 master data series contains requirements, which software can check automatically, for how organizations exchange product characteristics with each other. Whether you sell in automotive, food, or any global market, it gives your partners a shared definition of accurate, usable product data.
Some industries layer their own rules on top. IATF 16949, used across the automotive supply chain, builds on ISO 9001 and adds stricter defect prevention and waste reduction. AS9100 does the same for aerospace and defense, with added risk and configuration management. When every supplier in a chain works to the same base standard, consistency becomes part of how the industry operates. That is one reason automotive suppliers often keep fitment and specification records in a dedicated PIM for automotive parts and compatibility data.
Where Compliance Breaks Down: Product Data
All of these standards assume your product data is accurate, version-controlled, and traceable. In most manufacturing companies, that data is split across systems that do not talk to each other: ERP, CAD and PLM tools, the QMS, spreadsheets, and distributor portals.
The symptoms are familiar. Marketing descriptions do not match the technical specs. Compliance documents go missing between departments. Every product update means re-entering the same information in several places. And the workload is already heavy: more than 63% of U.S. manufacturers say they spend more than 2,000 hours a year complying with federal regulations alone, according to the NAM Manufacturers’ Outlook Survey (Q2 2023).

Scattered documentation does more than create audit findings. Customers lose confidence when your information does not line up, and failures can lead to recalls or financial losses that undo the trust certification was supposed to build.
During ISO 9001 and ISO 13485 audits, auditors check that product data (specs, certificates, revision history) is accurate, current, and easy to find. Internal audits can catch problems before the certification audit, but only if the data is clean and kept in one place. If it is not, the result is audit findings, corrective actions, and in regulated industries, possible loss of market access.
ISO 8000 adds another layer for anyone sending data to distributors and digital showrooms. It expects data to be portable, mean the same thing in every system, and work across the supply chain. Those are exactly the qualities that disappear when product data lives in many spreadsheets and someone has to merge product data from multiple sheets by hand.
Spreadsheets and the Audit Trail
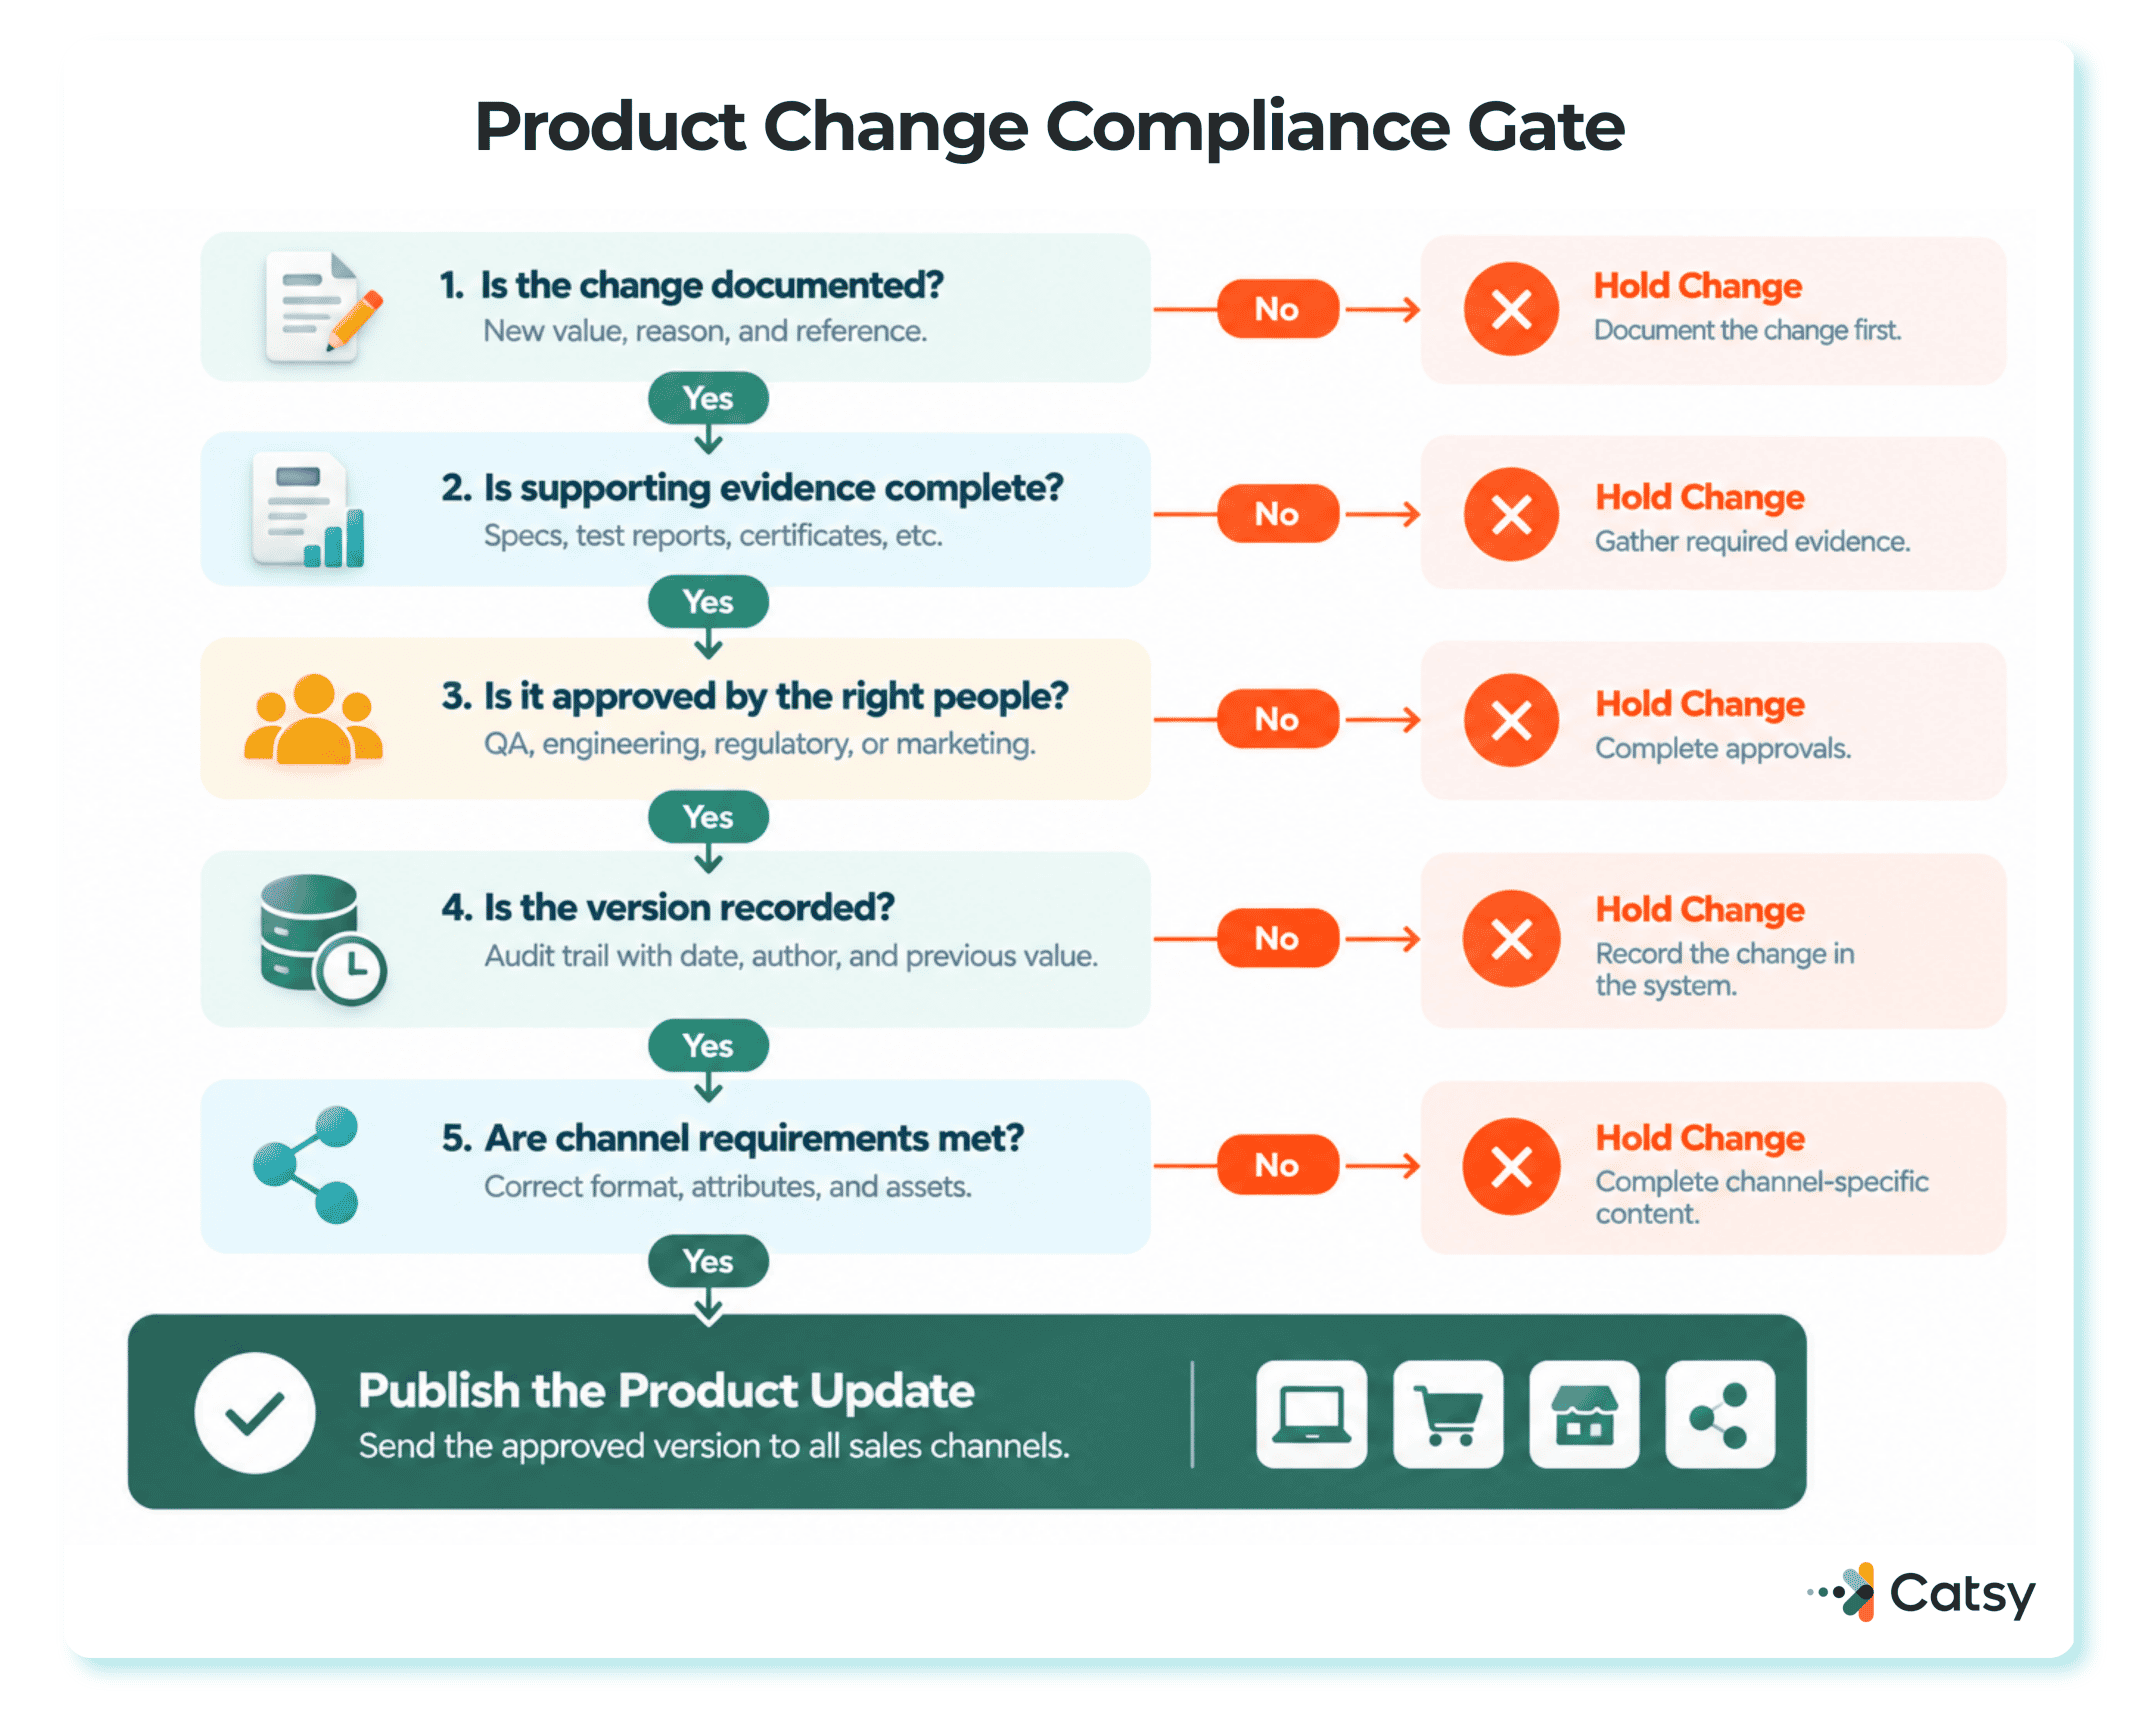
Auditors rarely stop at “what does the spec say?” They want the audit trail: a record of who changed it, when, what it said before, and who approved the change. ISO 9001 requires companies to control changes to their documented information. Clause 6.3 of ISO 9001:2026 puts even more weight on how QMS changes are planned and controlled.
For FDA-regulated electronic records, the rule is spelled out. 21 CFR 11.10(e) requires secure, computer-generated, time-stamped audit trails that record when users create, change, or delete records.
Shared spreadsheets were not built for this. Here is how they compare with a governed PIM record when an auditor starts asking questions:
| Auditor’s Question | Shared Spreadsheet | Governed PIM Record |
|---|---|---|
| Who changed this value? | No reliable tracking once files are copied, emailed, or shared | Each edit tied to a named user and role |
| When did it change? | No time-stamped history for individual cells | Time-stamped change log for each attribute |
| What did it say before? | Old values are overwritten unless someone saved a copy | Earlier versions kept and restorable |
| Who approved it? | Approval happens in email, outside the file | Approval recorded with the change |
| Which version did distributors get? | Several copies circulate, with no single master | Every channel is published from one source |
Without that evidence, teams spend the week before an audit rebuilding history from inboxes and file names. Anything they cannot prove can turn into a nonconformity.
What Non-Compliance Costs
A failed audit is rarely a one-time event. A major nonconformity leads to corrective action, follow-up audits, and possible certificate suspension, which can hold up supplier approvals and contract renewals. In medical devices, the consequences are heavier:
- Losing market access. Canadian device licensing depends on a valid MDSAP certificate. In the EU, selling depends on showing a compliant quality management system under the Medical Device Regulation.
- FDA enforcement. Since February 2, 2026, device manufacturers selling in the U.S. must comply with the QMSR, and an ISO 13485 certificate does not exempt them from inspection.
- Recalls caused by data errors. In 2025, the FDA classified a Class 2 recall of surgical kits where the firm cited incorrect product information inserts that created a risk of infection or allergic reaction. [TO FILL: this specific 2025 recall record could not be matched to a verifiable primary FDA source during this pass — original text preserved]
None of these began on the production line. Each one traces back to product information that was wrong, out of date, or impossible to prove when someone asked for it.
Closing the Gap With PIM
A Product Information Management (PIM) system is software that keeps all product data in one governed place. That includes specs, certificates, compliance documents, digital assets, and the content each sales channel needs. A QMS or ERP alone is not built to manage that data from creation all the way to the channels where customers see it. A PIM for manufacturers is.
In ISO terms, a PIM platform built for multichannel data governance helps in five practical ways.
One controlled record. Every attribute, certificate, and revision lives in one place with full version control. That supports ISO 9001’s documentation rules, ISO 13485’s device history records, and ISO 8000’s expectations for portable, accurate data. Strong product data governance adds validation rules, clear ownership, and role-based access so the data stays intact after it is entered.
History on demand. A PIM keeps a full change log. If an auditor asks what the specification for a SKU was on a given date, the answer takes seconds instead of days. Audit preparation becomes routine work, not a last-minute scramble.
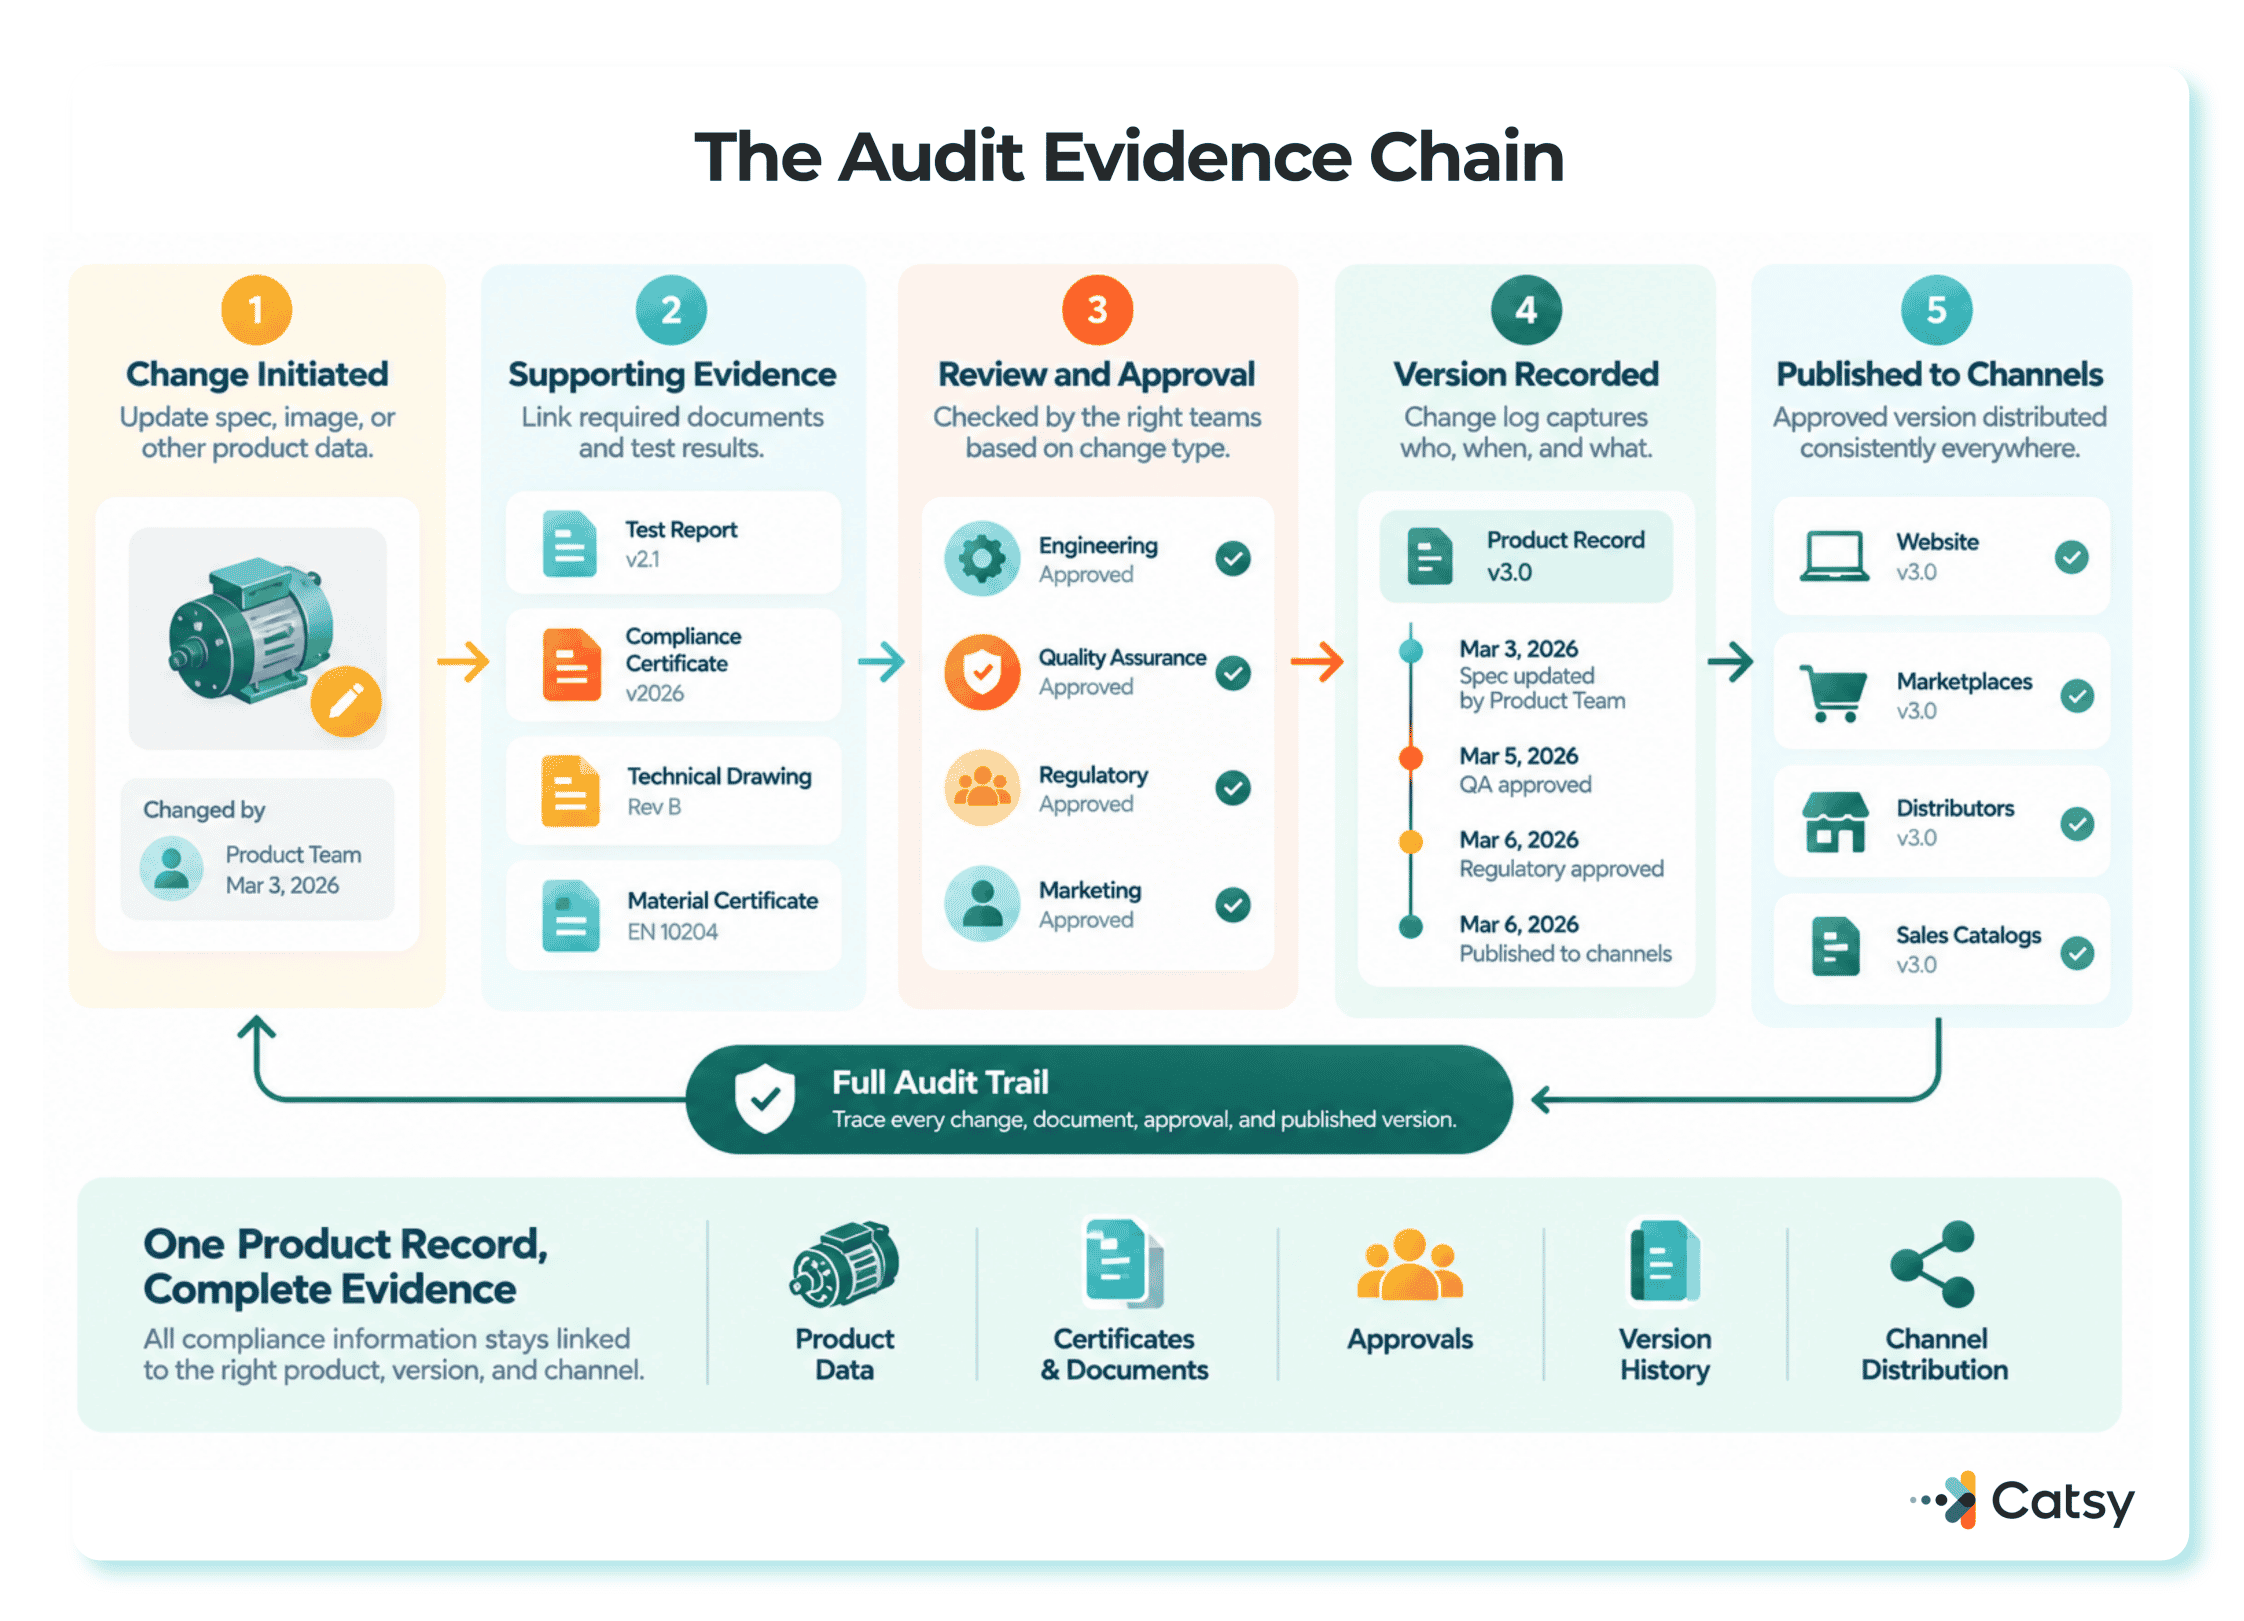
The same data on every channel. Compliance does not stop at the factory gate. When a PIM publishes, or syndicates, product data to distributors, retailers, and digital showrooms, every channel gets the same verified content from one source. Compliance declarations stay intact on the way, and consistent content also supports PIM-driven SEO optimization for product content.
Compliance documents next to the product. Safety data sheets, certificates, and regulatory filings can sit inside the product record instead of in a separate system that sales and marketing cannot reach. Digital asset management (DAM) is software for storing files such as images and PDFs. When DAM is built into the PIM, certificates, test reports, and technical drawings stay linked to the SKUs they belong to.
Sign-off before anything goes live. Approval workflows require the right people to review a change before it is published. It is the data version of a QMS sign-off, and it keeps unapproved changes away from customers and distributors.
Catsy’s PIM for manufacturers puts these ideas into specific features:
- Version control on bills of materials (BOMs, the list of parts and materials in a product) with a full audit trail
- Engineering change order (ECO) workflows with detailed approval logs
- Compliance attributes with built-in validation
- Role-based permissions down to the attribute, SKU, or asset level
- Pre-built ERP connectors that bring in part numbers and status data
- A login-controlled distributor portal that records who downloaded which product data and when
With ISO 9001:2026 asking more of change management, that combination gives quality teams a recorded, reviewable trail for every product change. Manufacturers who run compliance this way spend less time preparing for audits and see fewer mismatches between channels. Meeting ISO 9001, ISO 13485, and ISO 8000 becomes part of how they manage product data every day, not a separate project.
See how Catsy keeps product data audit-ready: version control, approval workflows, and full change history for every SKU, in one PIM and DAM platform. Book a Demo.
PIM, ERP, PLM, and QMS Each Hold Different Evidence
Manufacturers often ask whether they need PIM or ERP for ISO 9001. Usually the answer is both, because each system owns a different part of the evidence.
- ERP (enterprise resource planning) runs operations: SKUs, costs, inventory, purchasing, and supplier records.
- PLM (product lifecycle management) manages engineering: CAD files, BOMs, and engineering change orders.
- QMS software manages quality processes, such as nonconformances, CAPA (corrective and preventive action), internal audits, and training.
- PIM manages the controlled product record that customers and partners see.
| System | ISO Evidence It Supports | Where It Falls Short for Product Data |
|---|---|---|
| ERP | Supplier evaluation, purchasing controls, lot and inventory traceability | Not built for rich specs, certificates, or publishing to channels |
| PLM | Design controls, engineering revision history, design transfer | Internal-facing, so approved specs still need a controlled path to channels |
| QMS | Process control, corrective action, audit management | Does not hold or publish the product record customers and distributors see |
| PIM | Controlled product information, change logs, approval records, consistent publishing | Depends on clean inputs from ERP and PLM through integration |
The strongest setup connects them. Approved engineering data moves from PLM to ERP, and ERP feeds operational data into PIM. PIM then governs and publishes the product record, while the QMS runs the quality processes around it. That flow keeps SKU governance and supply chain transparency intact from design to the digital shelf. For more detail, see PIM vs ERP and PIM vs PLM.